WIRE home · World Instability · Business · Economics · Tech & Cyber · Orthodox · Archive · Subscribe
Download PDF · Dashboard image · All Technology & Cyber editions
UNCLASSIFIED // OPEN SOURCE | Friday, 23 October 2026 | Vol. 2026-296 | As of 230715 EDT OCT 26
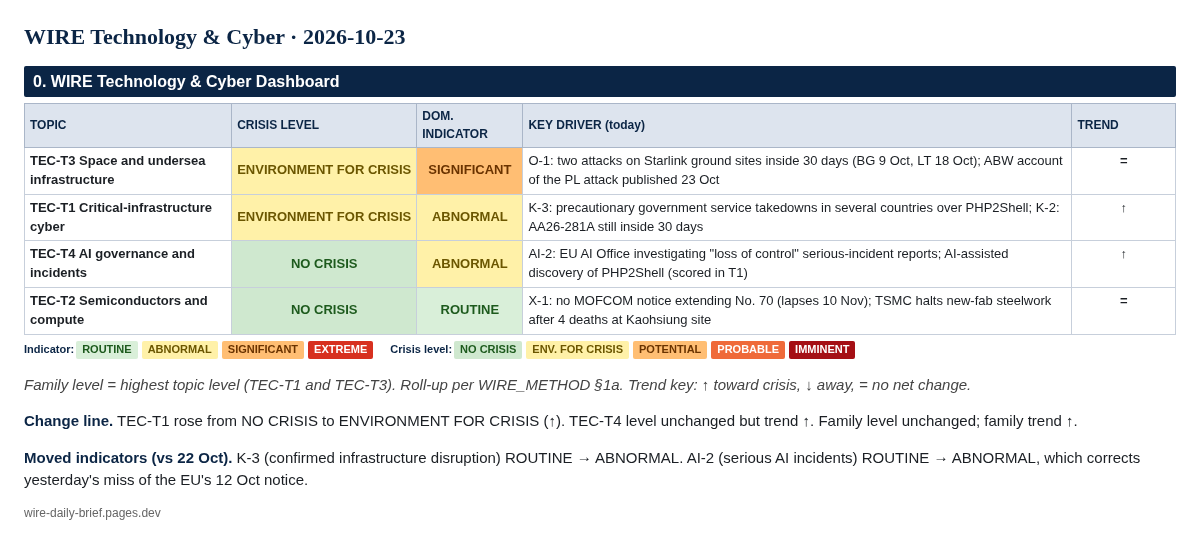
BLUF. The WIRE Technology & Cyber level holds at ENVIRONMENT FOR CRISIS, but the trend turns ↑ because critical-infrastructure cyber (TEC-T1) rose a level. On 21 Oct PHP shipped fixes for CVE-2026-109618 and CVE-2026-109619 ("PHP2Shell"), two unauthenticated remote-code-execution flaws affecting every PHP install that serves web requests. CISA told organisations to patch at once or take systems offline. The UK took 32 government services offline as a precaution, and South Korea raised its private-sector cyber alert level. Cloudflare reported millions of exploit attempts. Amazon says attempts began on 17 Oct, four days before the patch. No successful compromise has been confirmed, and neither CVE is in KEV yet. Space and ground-segment infrastructure (TEC-T3) stays at ENVIRONMENT FOR CRISIS (=): Poland's internal security agency published its full account of the Starlink arson today. Chips are NO CRISIS (=), 18 days before China's rare-earth suspension lapses. AI governance is NO CRISIS (↑) after an override.
| TOPIC | CRISIS LEVEL | DOM. INDICATOR | KEY DRIVER (today) | TREND |
|---|---|---|---|---|
| TEC-T3 Space and undersea infrastructure | ENVIRONMENT FOR CRISIS | SIGNIFICANT | O-1: two attacks on Starlink ground sites inside 30 days (BG 9 Oct, LT 18 Oct); ABW account of the PL attack published 23 Oct | = |
| TEC-T1 Critical-infrastructure cyber | ENVIRONMENT FOR CRISIS | ABNORMAL | K-3: precautionary government service takedowns in several countries over PHP2Shell; K-2: AA26-281A still inside 30 days | ↑ |
| TEC-T4 AI governance and incidents | NO CRISIS | ABNORMAL | AI-2: EU AI Office investigating "loss of control" serious-incident reports; AI-assisted discovery of PHP2Shell (scored in T1) | ↑ |
| TEC-T2 Semiconductors and compute | NO CRISIS | ROUTINE | X-1: no MOFCOM notice extending No. 70 (lapses 10 Nov); TSMC halts new-fab steelwork after 4 deaths at Kaohsiung site | = |
Family level = highest topic level (TEC-T1 and TEC-T3). Roll-up per WIRE_METHOD §1a. Trend key: ↑ toward crisis, ↓ away, = no net change.
Change line. TEC-T1 rose from NO CRISIS to ENVIRONMENT FOR CRISIS (↑). TEC-T4 level unchanged but trend ↑. Family level unchanged; family trend ↑.
Moved indicators (vs 22 Oct). K-3 (confirmed infrastructure disruption) ROUTINE → ABNORMAL. AI-2 (serious AI incidents) ROUTINE → ABNORMAL, which corrects yesterday's miss of the EU's 12 Oct notice.
Facts. On 21 Oct, CISA urged organisations to patch CVE-2026-109618 and CVE-2026-109619 "immediately" (fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35). It said systems that cannot be updated, including PHP 8.1 and older, should be taken offline. CISA said it had not yet observed exploitation (CISA alert, 21 Oct). The UK cybersecurity minister told Parliament that 32 government services had been taken offline, "largely" as a precaution. The NCSC sent 50,000 alerts and had no reports of successful hacks. South Korea activated emergency response measures, and China's industry ministry and Japan's prime minister urged patching. Cloudflare's chief executive reported tens of thousands of attempts in the first 45 minutes and "millions" by Thursday (Guardian, 22 Oct; NCSC). Amazon Threat Intelligence logged the first attempts on 17 Oct, while the flaw was still under embargo, and calls it "broadly exploited in the wild," though it is unclear whether any attempt succeeded. The PHP team brought its release forward after the CVE IDs and mitigation advice leaked. VirusTotal tracks more than 5.1 million exposed PHP hosts (BleepingComputer, 22 Oct). At 21:21 UTC on 22 Oct, Sophos withdrew its earlier report of a successful exploitation. Its telemetry shows scanning and failed attempts that tried to drop a Mirai-derived botnet ("Potassium") (Sophos). Neither CVE was in the KEV feed at 07:10 EDT. KEV added 6 entries from 19 to 22 Oct, all on 20 Oct, and none since (CISA KEV feed). CISA's directives page lists no new emergency directive (CISA directives). Ransomware.live recorded 255 leak-site victims from 16 to 22 Oct, against an 8-week mean of 232 (+10%) (ransomware.live data). The only Item 1.05 8-K this month is still Park Dental Partners (13 Oct) (EDGAR). Indicators. K-1 KEV/ED: ROUTINE (6, no ED). K-2 state-actor joint advisory: ABNORMAL (AA26-281A, 8 Oct). K-3 infrastructure disruption: ABNORMAL (↑; government services offline in several countries, precautionary, with no confirmed compromise and no utility, pipeline or hospital chain affected). K-4 ransomware: ROUTINE (+10%). K-5 Item 1.05: ROUTINE (1). Roll-up: 2 Abnormal = ENVIRONMENT FOR CRISIS (↑). Analyst Comment. The disruption so far comes from defenders taking systems down, not from attackers. The real risk sits in the long tail: schools, councils and charities running old PHP that the patch does not cover. Once a reliable public exploit appears, mass web-shell and botnet installs are likely within days, and some will land on systems with OT or health-sector links. K-1 would reach ABNORMAL if CISA adds the CVEs to KEV, and SIGNIFICANT if it issues an emergency directive. A confirmed hospital or utility compromise would make K-3 SIGNIFICANT and lift the topic to POTENTIAL CRISIS.
Facts. Today, Poland's ABW published its account of the 23 Sep Wola Krobowska fire. Two masked people got through the fence, poured accelerant on the station's control equipment and left after about three minutes. Two Turkish citizens living in Germany entered Poland via Świecko and returned to Germany afterwards. They were charged on 7 Oct with acting for a foreign intelligence service and with sabotage, and the investigation also covers earlier reconnaissance of the site and the people who ordered the attack (ABW, 23 Oct). No new ground-station attack has been reported since Vilnius on 18 Oct (Reuters via Yahoo, 18 Oct). In Taiwan, the SJC2 cable (Hong Kong direction, fault on 16 Oct), Taiwan–Matsu No. 2 (6 Oct) and TPE (2 Oct) are still awaiting repair. None has an official sabotage attribution (Taiwan cable status map). Indicators. O-1 attributed sabotage: SIGNIFICANT (2 in 30 days). O-2 GNSS interference: ROUTINE. O-3 counterspace: ABNORMAL (Cosmos 2612 approach on 17 Oct). Roll-up: ENVIRONMENT FOR CRISIS (=). Analyst Comment. The ABW mentions reconnaissance and commissioners, which supports yesterday's judgment that a single tasking hand is behind the attacks. The 23 Sep event falls out of the 30-day window today, but two events remain inside it, so the level holds.
Facts. The European Commission said on 12 Oct that the AI Office had requested and received serious-incident reports, and had sought information on security practices, from the developers of models involved in recent incidents it describes as "loss of control." It has not named the companies or models and has made no infringement finding (European Commission, 12 Oct). On 22 Oct, Parliament's centrist groups split over reviving AI liability rules (Politico Europe, 22 Oct). Wiz, which co-discovered PHP2Shell, said frontier AI models "substantially reduced" the barrier to building a working exploit (Guardian, 22 Oct). No new Federal Register AI action appeared on 21–23 Oct (Federal Register API). Indicators. AI-1 regulatory actions: ABNORMAL (DHS DeepSeek order, 20 Oct). AI-2 serious AI incidents: ABNORMAL (↑; officially acknowledged reports, effects unknown). AI-3 cloud outage with a post-incident report: ABNORMAL (Google europe-west2). Formula: 3 Abnormal = ENVIRONMENT FOR CRISIS. Override −1 to NO CRISIS: none of the three has disrupted a critical service or market, and the EU has not said the incidents had effects outside testing. Analyst Comment. PHP2Shell is the first mass-impact case in which AI is credited with turning an old bug into a working exploit. It is scored only in T1, to avoid double counting. A further AI-credited critical exploit, or EU disclosure that an incident escaped testing, would remove the override.
Facts. MOFCOM's policy list, read on 22 Oct and running to 20 Oct, contains no instrument that moves the 10 Nov (No. 70) or 27 Nov (No. 72) dates (Nami Tech Solutions, 22 Oct). BIS has published no export-control rule since 1 Oct (Federal Register). On 20 Oct, four workers died during steel hoisting at TSMC's Fab 22 construction site in Kaohsiung. Regulators halted that work, and TSMC voluntarily paused similar steelwork at all its new Taiwan sites (Focus Taiwan, 21 Oct; CNA). Indicators. X-1: ROUTINE. X-2 TSMC revenue: ROUTINE (October data due ~10 Nov). X-3 materials: ROUTINE (watch 10 Nov). X-4 fab outage: ROUTINE (the stoppage is construction, not production). Roll-up: NO CRISIS (=). Analyst Comment. The construction pause could delay new capacity by weeks, but current output is unaffected.
None resolved today. TEC-01, TEC-02 and TEC-03 remain open (TEC-03's window opens 26 Oct). New (dated 2026-10-23; logged in the prediction ledger): - TEC-04: CISA adds CVE-2026-109618 or CVE-2026-109619 to the KEV catalog by 6 Nov 2026. 70%, likely. - TEC-05: By 20 Nov 2026, a national government cyber agency, or an affected organisation in an official statement or SEC filing, confirms at least one successful compromise via CVE-2026-109618 or CVE-2026-109619. 75%, likely.
CISA (PHP alert 21 Oct, KEV feed, directives page); NCSC; Guardian (22 Oct); BleepingComputer (22 Oct); Sophos CTU; ransomware.live; SEC EDGAR; ABW (23 Oct); Reuters via Yahoo (18 Oct); smc.peering.tw; European Commission (12 Oct); Politico Europe (22 Oct); Federal Register; Nami Tech Solutions (22 Oct); Focus Taiwan (21 Oct); CNA.
WIRE Technology & Cyber | WIRE Desk | Open-source analysis. Not investment, legal or voting advice. UNCLASSIFIED // OPEN SOURCE.
Every WIRE, every morning. Unsubscribe anytime.
Prefer the website? Subscribe on Substack.
WIRE home · World Instability · Business · Economics · Tech & Cyber · Orthodox · Archive · Subscribe