WIRE home · World Instability · Business · Economics · Tech & Cyber · Orthodox · Archive · Subscribe
Download PDF · Dashboard image · All Technology & Cyber editions
UNCLASSIFIED // OPEN SOURCE | Monday, 26 October 2026 | Vol. 2026-299 | As of 260715 EDT OCT 26
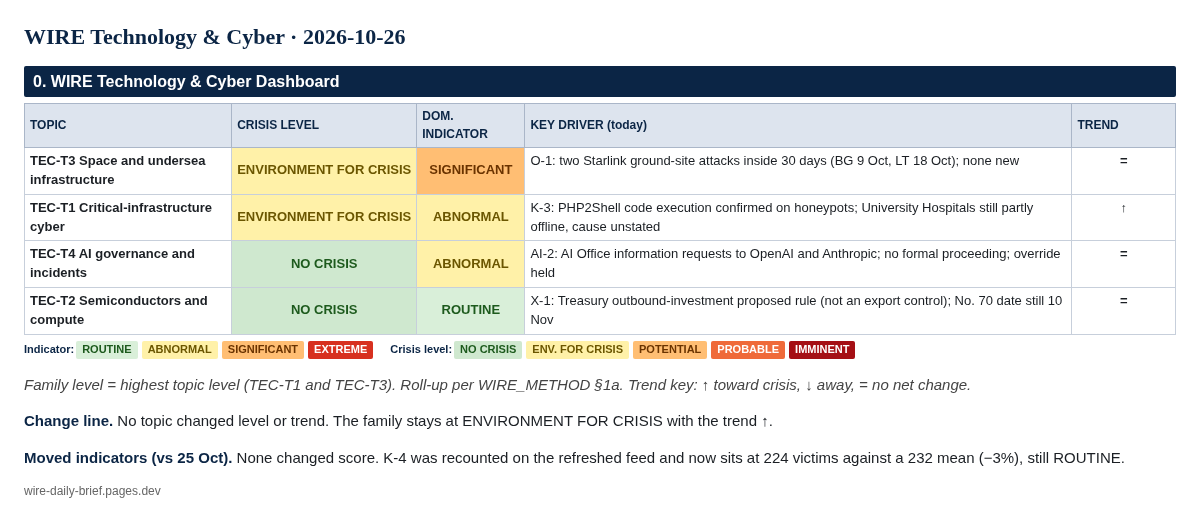
BLUF. The WIRE Technology & Cyber level holds at ENVIRONMENT FOR CRISIS (↑). PHP2Shell (CVE-2026-109618/-109619) exploitation is no longer only claimed by vendors. Honeypot data published on 24 Oct shows 35 shells spawned by Apache workers on decoy servers running PHP 8.4.26, and an independent researcher has endorsed the finding. PHP has also flagged CVE-2026-115560, a third remote-code-execution path that has no patch yet but needs an unusual configuration. CISA's alert still says it "has not observed successful exploitation," and neither CVE is in the KEV catalog. University Hospitals (Cleveland) has still not said whether it was attacked. Space and ground-segment infrastructure (TEC-T3) holds at ENVIRONMENT FOR CRISIS (=). AI governance (NO CRISIS, =) and chips (NO CRISIS, =) are quiet. Treasury has published its proposed outbound-investment rule.
| TOPIC | CRISIS LEVEL | DOM. INDICATOR | KEY DRIVER (today) | TREND |
|---|---|---|---|---|
| TEC-T3 Space and undersea infrastructure | ENVIRONMENT FOR CRISIS | SIGNIFICANT | O-1: two Starlink ground-site attacks inside 30 days (BG 9 Oct, LT 18 Oct); none new | = |
| TEC-T1 Critical-infrastructure cyber | ENVIRONMENT FOR CRISIS | ABNORMAL | K-3: PHP2Shell code execution confirmed on honeypots; University Hospitals still partly offline, cause unstated | ↑ |
| TEC-T4 AI governance and incidents | NO CRISIS | ABNORMAL | AI-2: AI Office information requests to OpenAI and Anthropic; no formal proceeding; override held | = |
| TEC-T2 Semiconductors and compute | NO CRISIS | ROUTINE | X-1: Treasury outbound-investment proposed rule (not an export control); No. 70 date still 10 Nov | = |
Family level = highest topic level (TEC-T1 and TEC-T3). Roll-up per WIRE_METHOD §1a. Trend key: ↑ toward crisis, ↓ away, = no net change.
Change line. No topic changed level or trend. The family stays at ENVIRONMENT FOR CRISIS with the trend ↑.
Moved indicators (vs 25 Oct). None changed score. K-4 was recounted on the refreshed feed and now sits at 224 victims against a 232 mean (−3%), still ROUTINE.
Facts. BleepingComputer reports that a researcher's honeypots recorded confirmed remote code execution against Apache mod_php on PHP 8.4.26. The researcher wrote that it is "now confirmed RCE with usable memory disclosure," and Expel researcher Marcus Hutchins called it "by far the highest quality confirmation" he has seen (BleepingComputer, 26 Oct). A summary of the 24 Oct honeypot report counts 35 shells on three decoys, coming from two commercial hosting IPs (Pillitteri, 26 Oct). On 23 Oct PHP published an informational advisory for CVE-2026-115560. It is a further RCE path that the 21 Oct releases do not fix, and the interim mitigation is session.upload_progress.enabled=0 (oss-security; Canadian Cyber Centre AL26-026 Update 1). CISA's alert (last revised 23 Oct) still says it "has not observed successful exploitation." The Canadian Cyber Centre reported "no active exploitation" as of its 23 Oct update (CISA alert). The KEV feed is unchanged (catalogVersion 2026.10.23, 1,756 entries, 8 additions in the week of 19–25 Oct), and PHP2Shell is absent (CISA KEV JSON). The latest emergency directive is still ED 26-03 (CISA directives). University Hospitals' last public statement, from the evening of 23 Oct, says it is reconnecting some partners and expects "some impact" into this week. It has not described a cyberattack (WKYC; Becker's). Ransomware.live counts 224 victims for 19–25 Oct, against a mean of 232 for the prior 8 weeks (ransomware.live). EDGAR shows one Item 1.05 8-K in October, Park Dental Partners (13 Oct) (EDGAR).
Indicators. K-1 KEV/ED: ROUTINE (8, no ED). K-2 state-actor advisory: ABNORMAL (AA26-281A, 8 Oct). K-3 disruption: ABNORMAL (the hospital-chain disruption has no confirmed cause, and exploitation is confirmed on decoys, not victims). K-4 ransomware: ROUTINE (−3%). K-5 Item 1.05: ROUTINE (1). Roll-up: 2 Abnormal = ENVIRONMENT FOR CRISIS. Trend ↑.
Analyst Comment. Working exploitation in the wild, three days after the patch, removes the main doubt about TEC-05 and TEC-04: the question was whether the exploit chain worked outside a lab. It is likely that CISA revises its "not observed" line and lists the CVEs in KEV within days. A KEV listing would also count toward TEC-03, though that call needs 10 additions in a single week. CVE-2026-115560 narrows the window for any organisation that patched without the mitigation. K-3 goes SIGNIFICANT only if a utility, pipeline or hospital chain is confirmed disrupted by an attack.
Facts. No new ground-station attack has been reported since Vilnius on 18 Oct, which Lithuania treats as Russia-linked sabotage (Reuters via Yahoo). Bulgarian warrants for two German nationals over the 9 Oct fires stand (DW, 19 Oct). Estonia's air navigation service lists NOTAM A2223/26, which warns of GNSS interference or spoofing in the Tallinn FIR and is valid to 13 Nov (EANS NOTAM area 24). No new attributed cable cut was found. Indicators. O-1: SIGNIFICANT (2 in 30 days; holds until 8 Nov). O-2: ROUTINE (standing Baltic NOTAM, no new bulletin). O-3: ABNORMAL (Cosmos 2612, 17 Oct). Roll-up: ENVIRONMENT FOR CRISIS (=). Analyst Comment. There is no change. Without a new attack, O-1 decays to ABNORMAL on 8 Nov. TEC-01 (60%) needs one new confirmed attack by 30 Nov.
Facts. The AI Office's information requests to OpenAI and Anthropic still show no formal proceeding or fine (Euronews, 14 Oct). Anthropic's status page logged several elevated-error incidents on 24–25 Oct, each resolved within hours (Claude status history). Indicators. AI-1: ABNORMAL. AI-2: ABNORMAL. AI-3: ABNORMAL (Google europe-west2, 20 Oct; the short Anthropic incidents do not raise it). Formula: ENVIRONMENT FOR CRISIS. Override −1 to NO CRISIS (held): no critical service or market has been disrupted by an AI incident, and there is no formal Commission proceeding. Analyst Comment. This topic is quiet. The agentic tooling seen in PHP2Shell intrusions stays scored under TEC-T1.
Facts. Treasury published a proposed rule implementing the Comprehensive Outbound Investment National Security Act. It would require notification of, or prohibit, US persons' transactions with foreign persons engaged in covered technologies. Comments close 7 Dec (Federal Register 2026-21786, 26 Oct). No new BIS chip rule was found. As of 19 Oct, MOFCOM's 2026 list showed no notice extending No. 70 past 10 Nov (technology.org, 19 Oct). Indicators. X-1 to X-4: ROUTINE (the outbound rule is investment screening, not an export control). Roll-up: NO CRISIS (=). Analyst Comment. The No. 70 date is 15 days out. A published MOFCOM notice remains the variable that matters for TEC-02.
None resolved today. Honeypot confirmation does not meet TEC-05, which requires an agency or a victim to confirm. TEC-01 to TEC-09 remain open. New (logged in the prediction ledger): - TEC-10: PHP releases fixed versions addressing CVE-2026-115560 on or before 13 Nov 2026. 70%, likely. - TEC-11: CISA revises its PHP2Shell alert, or issues a new product, stating it has observed successful exploitation, on or before 6 Nov 2026. 65%, likely.
BleepingComputer; Pasquale Pillitteri; oss-security; Canadian Centre for Cyber Security; CISA (alert, KEV JSON, directives); WKYC; Becker's; ransomware.live; SEC EDGAR; Reuters/Yahoo; DW; EANS; Euronews; Claude status; Federal Register; technology.org.
WIRE Technology & Cyber | WIRE Desk | Open-source analysis. Not investment, legal or voting advice. UNCLASSIFIED // OPEN SOURCE.
Every WIRE, every morning. Unsubscribe anytime.
Prefer the website? Subscribe on Substack.
WIRE home · World Instability · Business · Economics · Tech & Cyber · Orthodox · Archive · Subscribe