WIRE home · World Instability · Business · Economics · Tech & Cyber · Orthodox · Archive · Subscribe
Download PDF · Dashboard image · All Technology & Cyber editions
UNCLASSIFIED // OPEN SOURCE | Thursday, 29 October 2026 | Vol. 2026-302 | As of 290715 EDT OCT 26
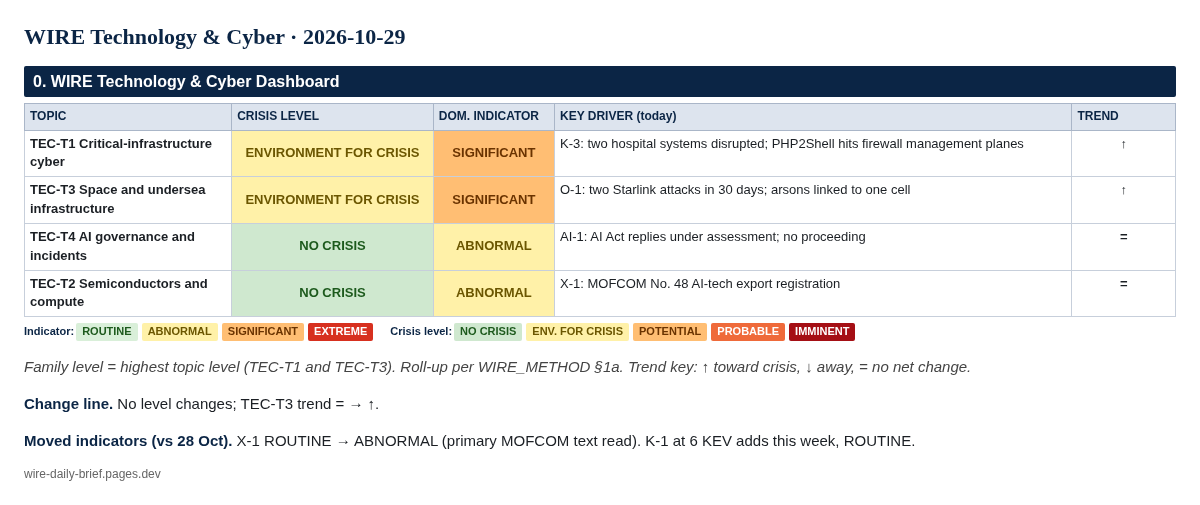
BLUF. The WIRE Technology & Cyber level holds at ENVIRONMENT FOR CRISIS (↑). PHP2Shell exploitation has reached firewall management interfaces; a research firm reports a suspected China-nexus operator reached Active Directory at a US government-affiliated organisation. No new hospital or utility disruption was found. Space infrastructure holds at ENVIRONMENT FOR CRISIS but turns ↑: Lithuanian prosecutors link the Vilnius, Sofia and Polish Starlink arsons to one suspected terrorist group. AI governance and chips stay at NO CRISIS (=); MOFCOM notice No. 48 is now verified from the primary text. No prediction falls due; TEC-16 and TEC-17 are new.
| TOPIC | CRISIS LEVEL | DOM. INDICATOR | KEY DRIVER (today) | TREND |
|---|---|---|---|---|
| TEC-T1 Critical-infrastructure cyber | ENVIRONMENT FOR CRISIS | SIGNIFICANT | K-3: two hospital systems disrupted; PHP2Shell hits firewall management planes | ↑ |
| TEC-T3 Space and undersea infrastructure | ENVIRONMENT FOR CRISIS | SIGNIFICANT | O-1: two Starlink attacks in 30 days; arsons linked to one cell | ↑ |
| TEC-T4 AI governance and incidents | NO CRISIS | ABNORMAL | AI-1: AI Act replies under assessment; no proceeding | = |
| TEC-T2 Semiconductors and compute | NO CRISIS | ABNORMAL | X-1: MOFCOM No. 48 AI-tech export registration | = |
Family level = highest topic level (TEC-T1 and TEC-T3). Roll-up per WIRE_METHOD §1a. Trend key: ↑ toward crisis, ↓ away, = no net change.
Change line. No level changes; TEC-T3 trend = → ↑.
Moved indicators (vs 28 Oct). X-1 ROUTINE → ABNORMAL (primary MOFCOM text read). K-1 at 6 KEV adds this week, ROUTINE.
Facts. Palo Alto Networks' advisory on PHP CVE-2026-109618/109619 now says "active exploitation has been observed" against internet-exposed PAN-OS management interfaces (PAN advisory; The Hacker News, 29 Oct). Dream Research reports an operator chained PHP2Shell with the Linux kernel flaw "Fragnesia" (CVE-2026-46300) to root 25 firewall servers in the US, Japan, Taiwan and South Korea on 23–24 Oct, then moved into a US government-affiliated organisation's firewall management server and Active Directory; Dream calls it suspected China-nexus (Dream Research; SecurityWeek, 28 Oct). CISA added CVE-2026-46300 (due 31 Oct, forensic triage required; it "can be chained" with the PHP CVEs "to implant PHP webshells and run commands as root") and VMware ESX CVE-2026-41709 on 28 Oct (CISA alert; KEV CSV). KEV catalogVersion 2026.10.28 has 1,762 entries, 6 added since 26 Oct (KEV JSON); no new emergency directive (CISA directives). PHP has not yet shipped a fix for CVE-2026-115560 (php.net). UNM says it "did not make concessions" and clinics are fully functional (UNM HSC, 28 Oct); whether patient data was taken awaits FBI forensics (Albuquerque Journal). University Hospitals: "Patients remain unable to access MyChart" (WKYC, 28 Oct). Ransomware.live: 106 victims 26–28 Oct vs an 8-week mean of 230/week (feed). Indicators. K-1: ROUTINE (6). K-2: ABNORMAL (AA26-281A; Dream's attribution is a vendor claim, not a government advisory). K-3: SIGNIFICANT. K-4: ROUTINE (on pace for about +7%). K-5: ROUTINE. Roll-up: ENVIRONMENT FOR CRISIS. Trend ↑. Analyst Comment. Exploitation of perimeter-device management planes is the pattern that preceded earlier edge-device emergency directives, so TEC-07 (25%) now looks conservative; it stands. A government attribution to a state actor would move K-2 to SIGNIFICANT and put POTENTIAL CRISIS in play.
Facts. On 29 Oct Lithuanian police and prosecutors named two Germany-resident men in their 20s, held in Germany at Bulgaria's request, as suspects in the 18 Oct Vilnius attempt, on suspicion of forming a terrorist group and a terrorist act, and linked them to the Bulgarian and Polish Starlink arsons (LRT/BNS, 29 Oct). Poland's interior ministry blames "Russian services" for the 23 Sep Wola Krobowska arson (MSWiA, 12 Oct). No new attack found. Estonian GNSS-interference NOTAMs remain in force into November (EANS). Indicators. O-1: SIGNIFICANT (2 in 30 days). O-2: ABNORMAL (Baltic GNSS warnings, carried). O-3: ABNORMAL (Cosmos 2612). Roll-up: ENVIRONMENT FOR CRISIS. Trend ↑. Analyst Comment. Three national investigations now point to one network that Poland attributes to Russian services, which fits a sustained campaign. Trend up, not level: no new attack and no outage.
Facts. On 28 Oct the Commission said it has the replies to all AI Act information requests whose deadlines have passed, from more than 30 companies. It announced no findings, penalties or timetable (2eu.brussels, 28 Oct). No major cloud outage was found on 28 Oct (incidents.fru.dev). Indicators. AI-1/2/3: ABNORMAL. Override −1 to NO CRISIS (held): no AI incident has disrupted a critical service, and no formal proceeding has been opened.
Facts. MOFCOM–MOST Announcement 2026 No. 48 (16 Oct) proposes adding 40 technologies to China's export prohibited/restricted catalogue, 23 in AI (large models, agents, compute clusters, information processing), and requires pre-export registration from publication; comments close 15 Nov (MOFCOM No. 48). No new BIS chip rule (Federal Register, 29 Oct). No. 70 still lapses 10 Nov on paper. Indicators. X-1: ABNORMAL. X-2 to X-4: ROUTINE. Roll-up: NO CRISIS (=).
Resolved: none due. TEC-05/11 open (vendor evidence only; KEV text says "can be chained"). TEC-06/12/13 open (UH still "cybersecurity incident", MyChart down). TEC-14 awaits FBI forensics; TEC-15 unconfirmed; TEC-03 at 6 this week. New (logged in the prediction ledger): - TEC-16: CISA, FBI or NSA, alone or in a joint advisory, publicly attributes PHP2Shell or Fragnesia exploitation to a PRC state-sponsored actor, by 30 Nov 2026. 25%, unlikely. - TEC-17: Lithuanian, German or Bulgarian authorities announce that at least one Vilnius suspect has been surrendered or extradited from Germany, by 31 Dec 2026. 60%, roughly even chance to likely.
Palo Alto Networks; The Hacker News; Dream Research; SecurityWeek; CISA (alerts, KEV, directives); php.net; UNM HSC; Albuquerque Journal; WKYC; ransomware.live; LRT/BNS; Poland MSWiA; EANS; 2eu.brussels; incidents.fru.dev; MOFCOM; Federal Register.
WIRE Technology & Cyber | WIRE Desk | Open-source analysis. Not investment, legal or voting advice. UNCLASSIFIED // OPEN SOURCE.
Every WIRE, every morning. Unsubscribe anytime.
Prefer the website? Subscribe on Substack.
WIRE home · World Instability · Business · Economics · Tech & Cyber · Orthodox · Archive · Subscribe